

Authentication
The Authentication tab decides how long a device that signed in with single sign-on (SSO) stays connected before its user has to sign in again. It holds two settings: Peer login expiration and Peer inactivity expiration.
Use them to make sure that a lost or shared laptop does not stay on your network forever. You find the tab under Settings > Authentication.
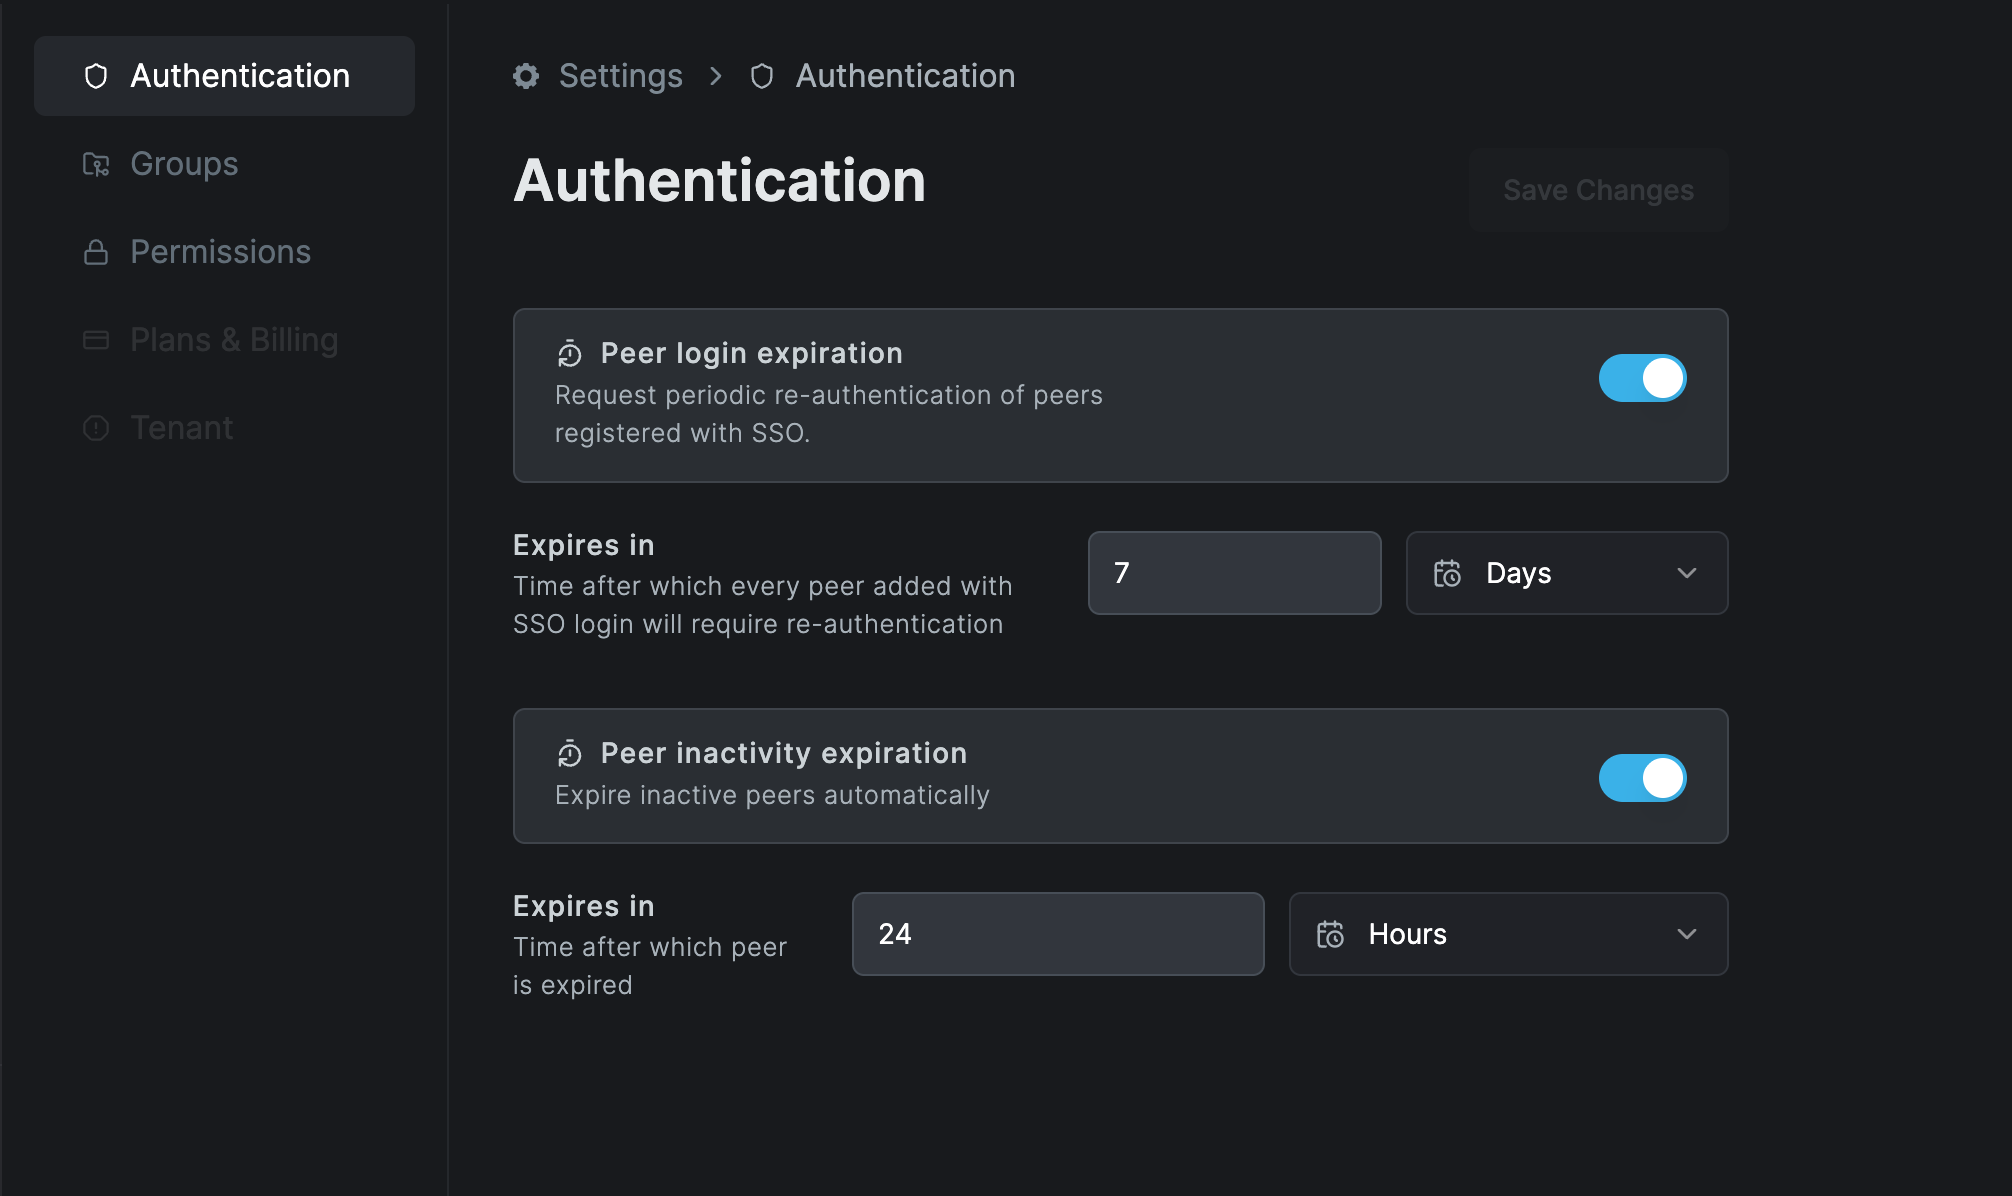
Both settings apply only to peers that were added with SSO, that is, a user signed in from the Netzilo client. Peers added with a setup key never expire, so servers and other unattended machines keep running.
How it works
- A user signs in from the Netzilo client. The device becomes a peer that belongs to that user.
- Peer login expiration counts from that sign-in. When the period ends, the peer is disconnected and shows Login required in Endpoint > Peers.
- Peer inactivity expiration counts while the peer is disconnected. A peer that stays offline longer than the period is expired in the same way.
- The user signs in again from the Netzilo client, and the peer reconnects with its groups and address unchanged. Nothing is deleted.
How a device signs in
A person signs a device in with Connect in the Netzilo desktop app (or the workplace
picker in its window), or with netzilo up or netzilo login on the command line.
- In a browser on the same computer. The client opens the Workplace's sign-in page in
the browser. After the sign-in at your identity provider, the result goes back to the
client on this computer, to a listener on
localhostonly, and the browser shows Login Successful, You will be taken to your workplace now., then opens the Workplace. If the sign-in fails, the page shows Login Failed and asks to close it and try again. Because the result goes to this computer only, a sign-in link opened on another machine signs nothing in. - With a code, from any device. When the browser is not on this machine, for example
over SSH or a remote desktop, run
netzilo up --device-code(ornetzilo login --device-code). The client prints a page address and a code. Open the page on any device, enter the code and sign in. - On a Linux machine without a desktop,
netzilo upalways prints an address and a code.
The desktop app signs the Workplace in with the client's own sign-in, so users do not sign in a second time in its window.
Set peer login expiration
- Go to Settings > Authentication.
- Turn on Peer login expiration.
- Under Expires in, enter a number and choose Days or Hours.
- Click Save Changes.
| Field | What to enter |
|---|---|
| Peer login expiration | On: every SSO peer has to re-authenticate after the period. Off: SSO peers stay signed in until the user logs out or the peer is removed. |
| Expires in | From 1 hour up to 180 days. The default is 24 hours. For laptops, 8 to 24 hours is a common choice. |
You can exempt a single peer, for example a shared workstation that a user signed in to. In Endpoint > Peers, open the row menu and choose Disable Login Expiration. The peer then shows Expiration disabled.
Set peer inactivity expiration
- Go to Settings > Authentication.
- Turn on Peer inactivity expiration.
- Under Expires in, enter a number and choose Days or Hours.
- Click Save Changes.
| Field | What to enter |
|---|---|
| Peer inactivity expiration | On: an SSO peer that has been disconnected longer than the period must sign in again. |
| Expires in | From 1 hour up to 180 days. |
Inactivity expiration suits contractors and occasional devices: a device that has not been used for a while cannot quietly reconnect weeks later.
What users see
When a peer expires, the Netzilo client disconnects and asks the user to sign in again: the
desktop app shows Netzilo Session Expired. The user clicks Connect in the desktop
app, or runs netzilo up on the command line. The device
then reconnects with its previous address and groups.
Troubleshooting
A server keeps disconnecting with "Login required". The server was added with SSO, so it follows the expiration period. Add servers with a setup key, or use Disable Login Expiration on that peer.
Saving fails with "peer login expiration can't be larger than 180 days". Choose a period between 1 hour and 180 days.
The browser sign-in finishes, but the device stays signed out. The sign-in was
finished in a browser on another computer, where the result cannot reach this device's
client. Sign in from a browser on the device itself, or run netzilo up --device-code.
Users are asked to sign in more often than expected. Check both settings. Inactivity expiration also expires a peer that was turned off for longer than its period.
Related Documentation
- Groups - Group propagation and JWT group sync
- Permissions - Portal access, AI Assistant, clientless access and published applications
- Peers - Peer list, Login required badge and per-peer expiration
- Setup Keys - Add machines that never expire
- Identity provider and SSO - Connect your company identity provider